A Guarded Terraform Pipeline with GitHub Actions and Azure OIDC
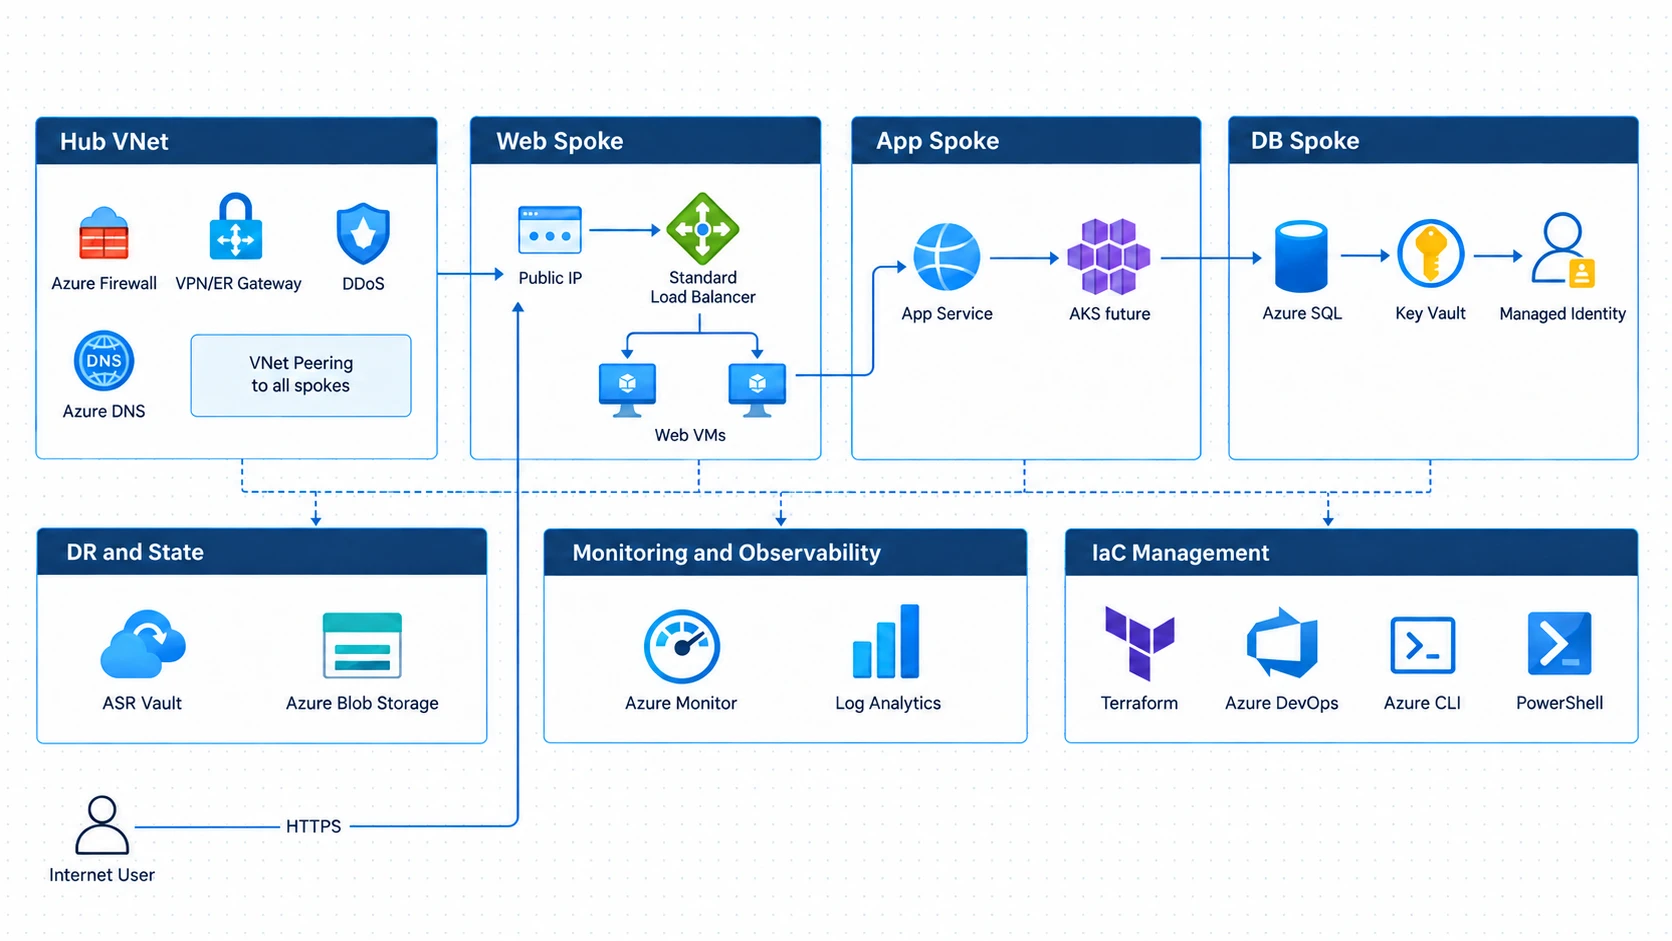
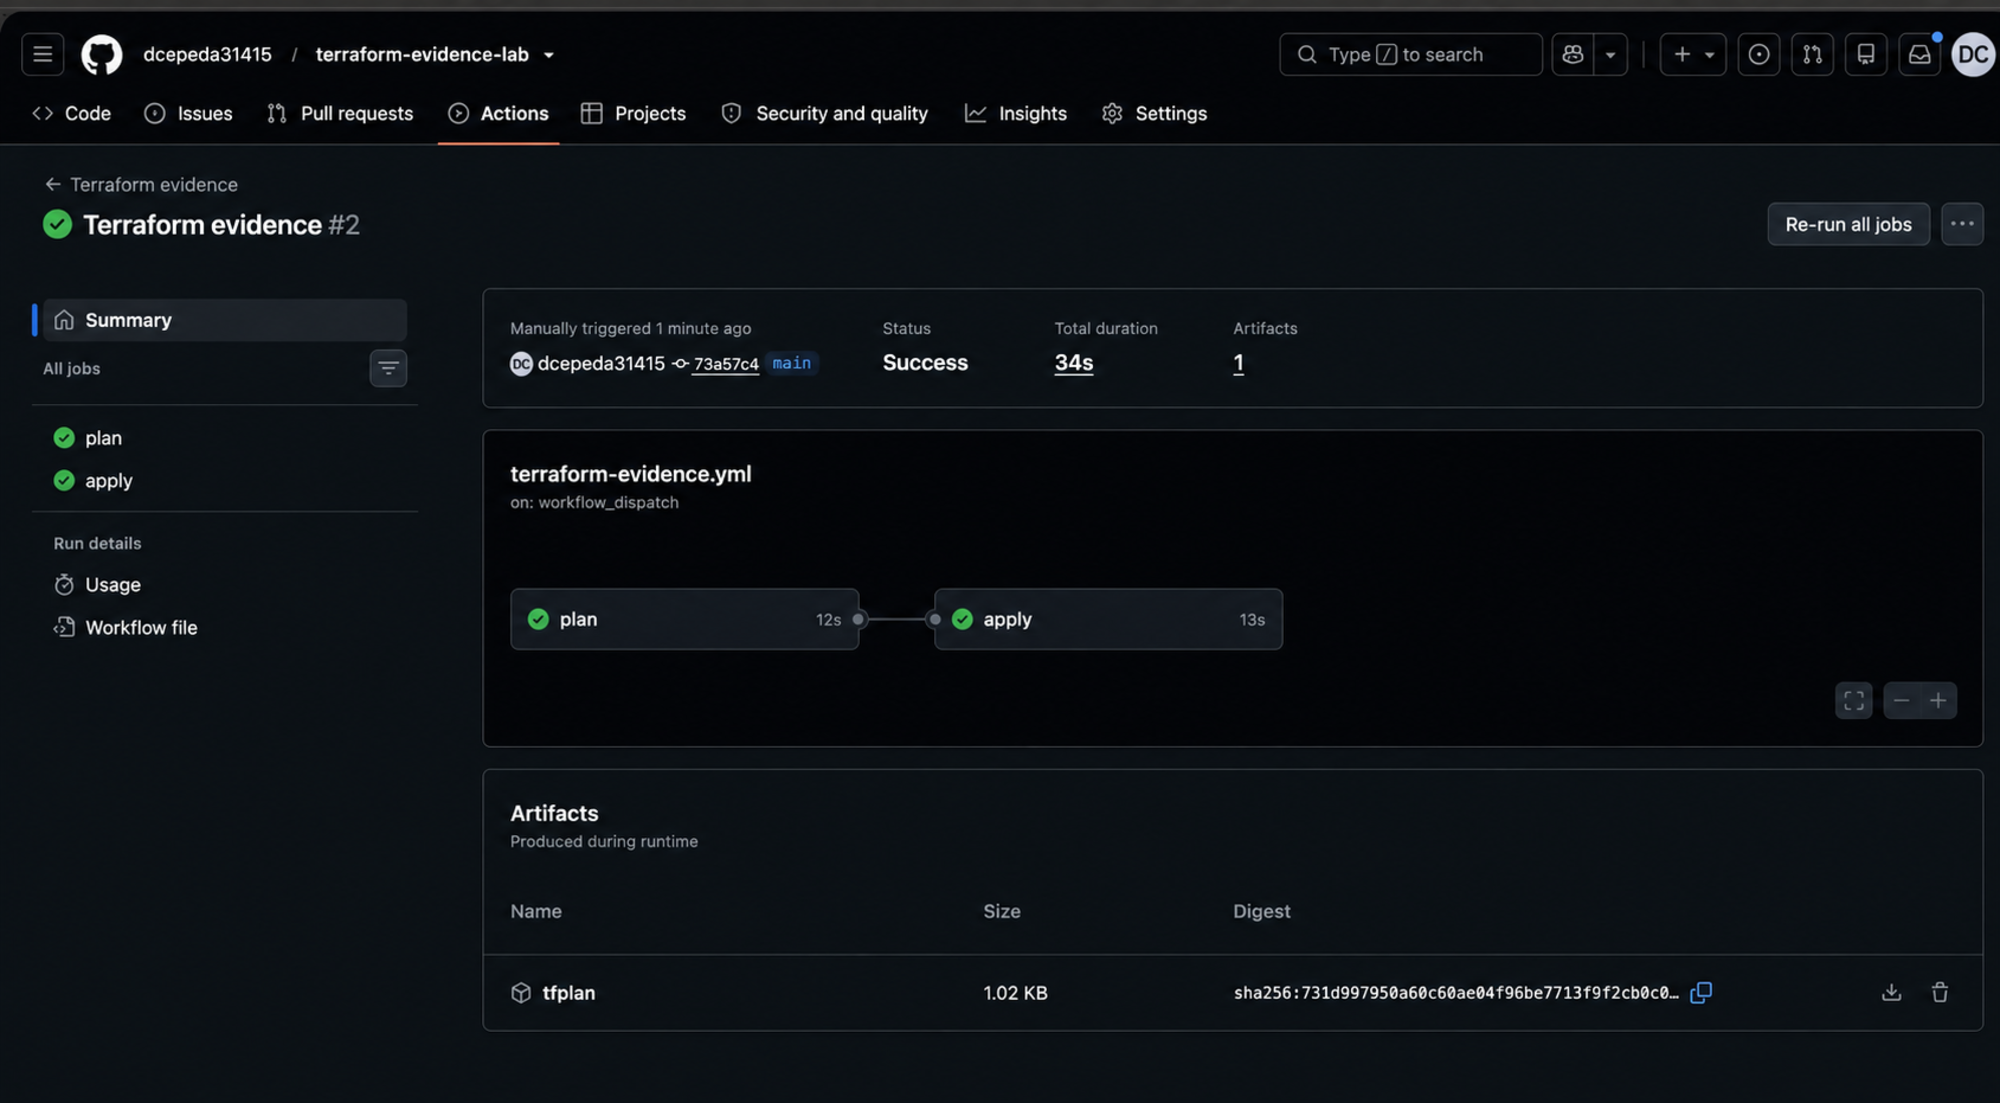
A Terraform pipeline should do more than run plan and apply. Production infrastructure needs controlled auth, one writer at a time, plans people can review, approval gates, post-deploy checks, and a clear recovery plan. I built that workflow with GitHub Actions and Azure. It uses OpenID Connect (OIDC) instead of a stored Azure client secret. It pins third-party actions to reviewed commits and applies a saved Terraform plan. I also kept a clear line between what the pipeline can prove and what the app architecture has to prove on its own. ...